
[ capabilities ]
What We Check In AI-Generated Code
AI tools tend to repeat the same security mistakes. We look for those first, then review the rest of your code by hand.

Exposed secrets & keys
AI tools often paste API keys and database credentials straight into the code. We find every exposed secret, help you rotate it, and move it somewhere safe.

Auth & access control
Login works in the demo, but can one user read another user's data? We test authentication, roles, and database rules the way an attacker would.

OWASP Top 10 checks
We check for SQL injection, cross-site scripting, and the other OWASP Top 10 risks that AI-generated code commonly misses.

Dependency & package risk
AI tools pull in packages without asking. We flag outdated, vulnerable, or non-existent dependencies before they turn into a problem.

Architecture & data exposure
We trace how data moves between your frontend, backend, and third-party services, and close the paths that expose more than they should.

Fixes & re-testing
An audit only helps if the issues get fixed. Our developers can fix what we find, starting with the critical issues, then re-test to confirm they're closed.


[ process ]
How The Audit Works
A clear scope, a real review, and a report you can act on, without weeks of back and forth.

[step 01]
Scope & access
We agree what's in scope, get read access to your code and hosting, and note which AI tools built which parts of the app.

[step 01]
Scan & manual review
Automated scanners catch the obvious issues. Our developers then review the code by hand for the logic and access flaws scanners miss.

[step 01]
Risk report
You get a plain-language report with every issue ranked by severity, plus what it would take to fix each one.

[step 01]
Fix & re-test
If you want us to, we fix the critical and high-risk issues first, then re-test to confirm they're closed before handing back.
[ stacks ]
The Stacks We Review
AI tools generate code in many frameworks. We review the stacks they most often produce, using scanners alongside manual review.


[ case studies ]
Case studies


Realty
[
Estora
]
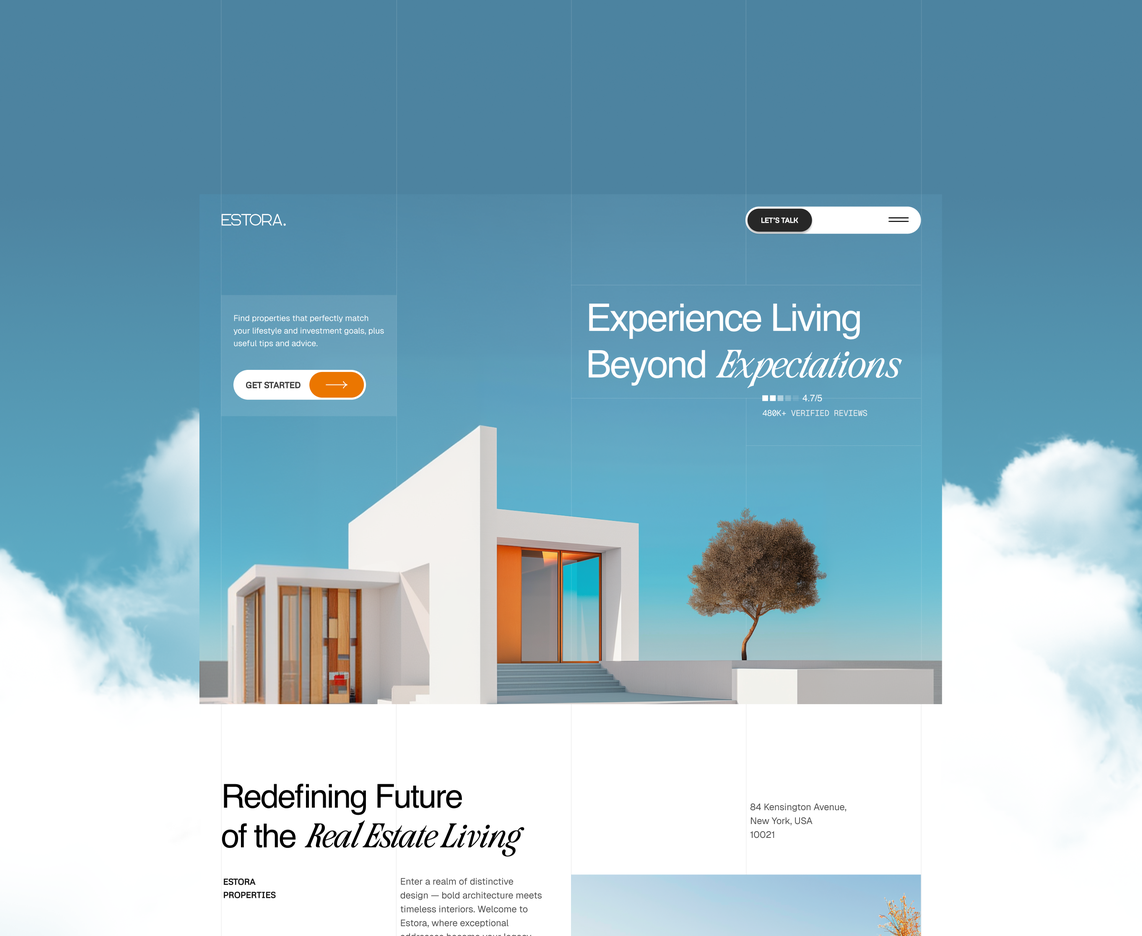
A luxury property site that turns viewers into buyers
Rescue and modernization build · 4-week engagement period · Mobile-first relaunch plan
[ The challenge ]
Estora’s old site buried its best residences under slow pages and weak calls to action, so serious buyers left before they ever reached out to the sales team.
Next.js
Typescript
Tailwind CSS
Vercel
[ What we built ]
A refreshed responsive site with a sharp hero, featured residence pages, client stories, and clear contact paths, all served from a much faster front end.
2.4x
Viewing requests
-39%
Bounce rate
96
Speed score
Responsive website · UI/UX & front-end development
[ projects ]
Projects We've Rescued And Rebuilt


CARTIVO
Website
Video Commerce
Fresh code for a shoppable video platform
Cartivo had a strong idea held back by a tired website. We refreshed it end to end, with shoppable videos, live events, and clear metrics, and now e-commerce teams book demos with ease.

ROVA
Website
Furniture
Reviving a furniture brand’s online showroom
Rova’s furniture deserved a better stage than its old pages gave it. Our team modernized the site so every piece gets room to breathe, and visitors move from first look to the full collection.
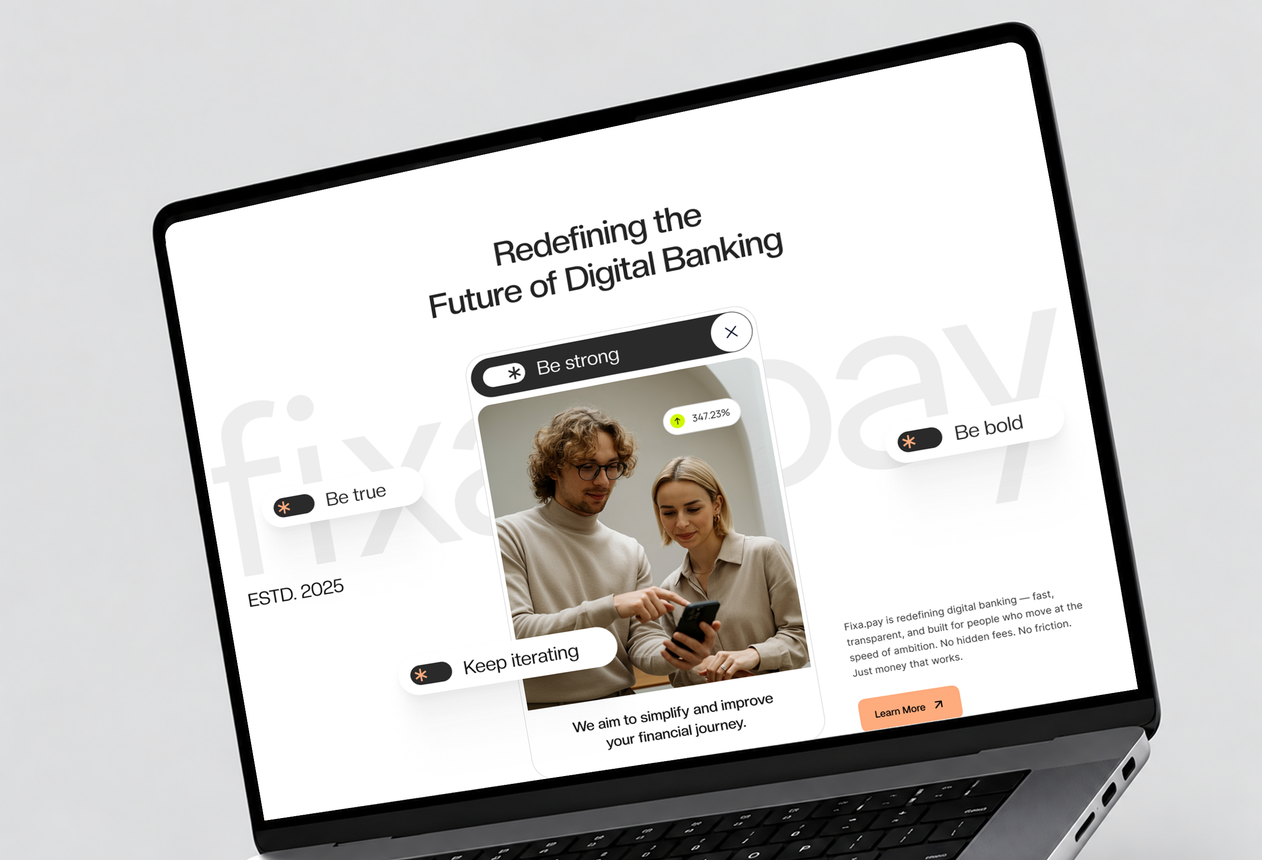
FIXA.PAY
Website
Fintech
Giving a digital bank a faster front door
The product was fast, but the old site felt slow and unclear. We rebuilt it around clean feature stories and real proof, including 500K+ daily transactions, so a complex offer now reads with confidence.
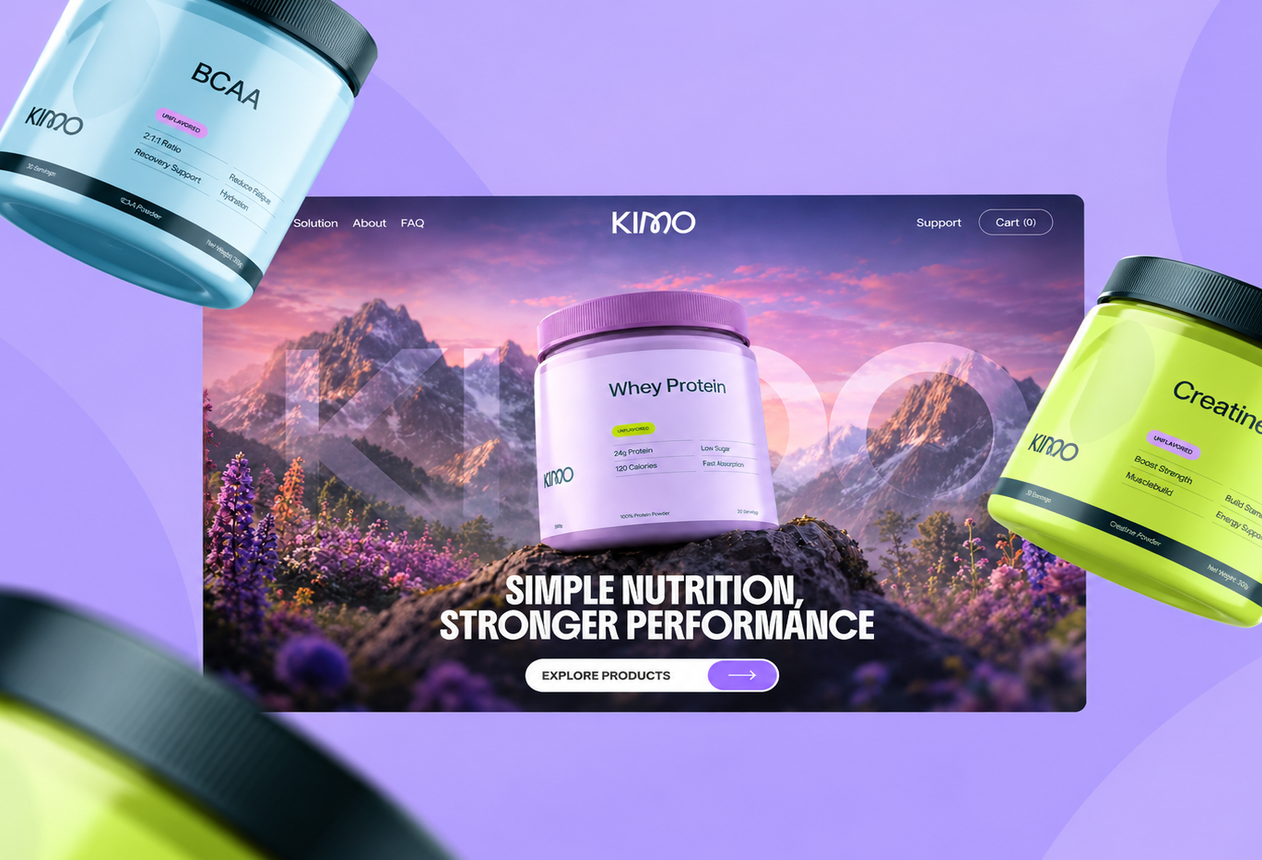
KIMO
Website
Health & Nutrition
A supplement store rebuilt for serious athletes
Kimo’s old site looked like every other supplement shop. We rebuilt it from the ground up with clinical stats, product cards, and community reviews, so athletes can trust the range and buy in minutes.
[ transformation ]
The Rebuild, Not The Pitch
Projects often begin with damage control: the audit, the fix, and the aftermath.
A dedicated 4-person pod
Designer, engineers and QA, all on your product.
One team, two platforms
iOS + Android, one team, one codebase.
Crash-free at scale
99.2% stability across 1.8M live users.
What clients actually say
Feedback from founders we've shipped with.
Direct speak with the engineer
Saiful replies directly, no manager in the loop.
Built in Dhaka, shipped globally
Live in 9+ countries across four continents.
[ testimonial ]
What It's Like Working With Us
Sofia Gouveia @ Esdiac
Design Director
We relied on them to build our online store with AI-enhanced features that improve customer experience.
Working with Dev Monks on our ESDIAC app and group websites was an excellent experience. They were patient, attentive to feedback, and delivered clean, consistent, high-quality work. We're proud of the results and happy to continue our long-term partnership with them.

Anika @ Coin Pulse
Founder
Their team truly understood our vision and brought it to life through a stunning digital identity.
Dev Monks is a professional, reliable partner for end-to-end product builds. From clean, modern designs to seamless development, they exceeded my expectations. I couldn't be happier with the collaboration!
Austin @ Clarity LLC
CEO
Working with Dev Monks completely changed how we approached building our app website scratch.
I've worked with Design Monks on three websites, and they've been nothing but exceptional. Their design is top-notch, development is reliable, and communication is always smooth. They quickly act on feedback and deliver exactly what I need. For me, they're a 10/10 partner for all things design and development.
Ted Nash @ Yenex
Founder & CEO
I never expected building a complex platform to feel this easy and smooth.
I've had the pleasure of collaborating with Dev Monks for a while now on my new project. They're lightning-quick in addressing any questions or feedback I have, and they consistently go the extra mile to make sure I'm thrilled with the final outcome. I wholeheartedly endorse them


[ faq ]
Questions You'd Ask Before Signing Off

How is this different from Rescue & Modernization?

Rescue & Modernization fixes code that's broken, slow, or outdated. The AI Code Security Audit answers one question: can someone misuse your app or its data? Many teams start with the audit and move into rescue work only if they need it.
Which AI tools' code do you audit?
Code from Lovable, Bolt, v0, Replit, Cursor, Claude Code, GitHub Copilot, and similar tools, as well as code written by hand. The stack matters more than the tool, and we'll confirm we cover yours on the first call.
Do you fix the issues too?
Yes, if you want us to. The report works on its own, so your own team can fix the issues, or our developers can fix them and re-test.
What access do you need?
Read access to your code repository and, ideally, to your hosting and database settings. We only ask for what the audit needs, and you can remove access when we're done.
Does an audit guarantee my app is secure?
No audit can promise that. It finds and ranks the issues present when we review the code, so you can fix the ones that matter most. We recommend a fresh check after major changes.


[ start project ]
Not Sure If Your AI-Built App Is Safe?
Tell us what you built and which tools you used. We'll tell you honestly what an audit should cover and what it will take.
Typical range
$15,000 – $80,000
~/devmonks/stack.ts

Dual-store launch included

Fixed, transparent scope
Your ideas deserve more than prototypes. Partner with Dev Monks and bring scalable, reliable, and AI-enhanced products to life today.


